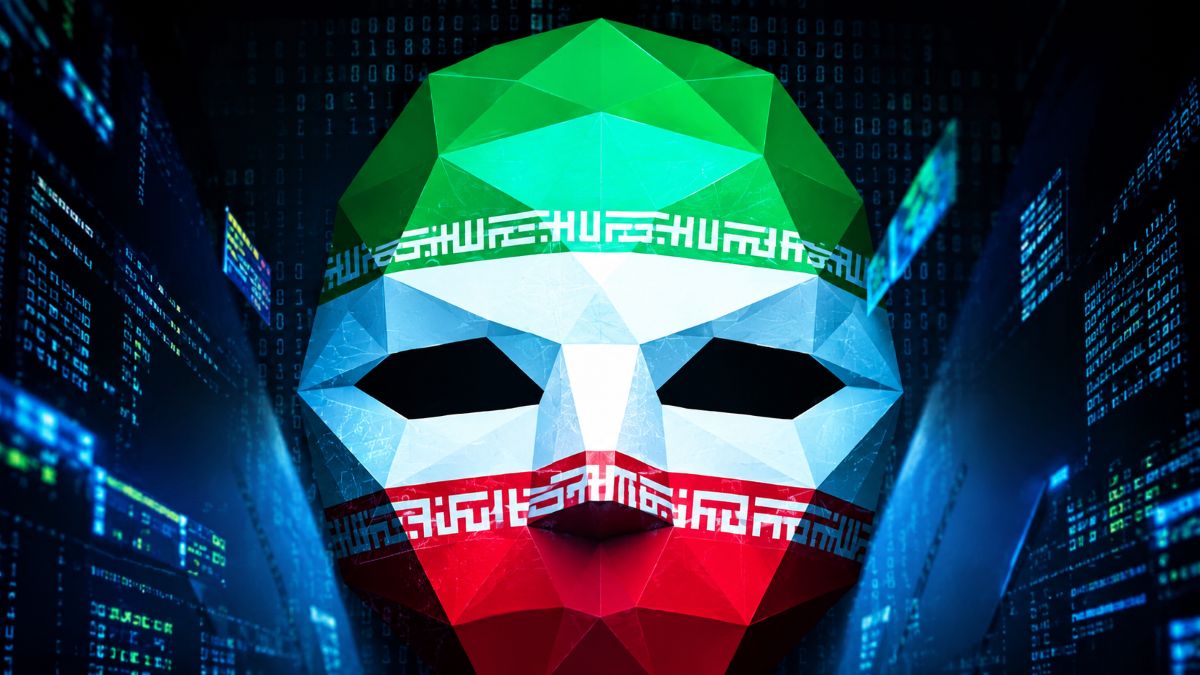

WASHINGTON: Cybersecurity firm Semperis says Prince of Persia hackers used a command-and-control server hosted in the United States after returning from a months-long pause. The Iranian state-linked group is also tracked as Infy.
It has operated for nearly two decades and has mainly targeted Iranian dissidents. Its targets have also included government and private organisations in the United States, Europe and the Middle East.
Semperis researcher Tomer Bar identified the US-based server in August. He said it was the first such infrastructure found inside the country since 2016.
The group resumed operations on May 27 after pausing for about three months, according to the research. Within a week, one malware tool extracted more than 1,800 files from a single victim.
Read: Hackers release files indicating NSA monitored global bank transfers
Bar said the number of known victims remained small. That could point to highly targeted attacks or difficulty compromising new systems.
Semperis said the group changed its hosting strategy after returning. It moved away from virtual private servers and began using shared hosting in the United States.
Read: Microsoft Warns of Cyber-Espionage Campaign with Ransomware Targeting SharePoint Vulnerability
Researchers linked the US server to Tornado, one of the group’s newer malware families. Tornado can steal files through Telegram-based channels.
“This is the last place we expected to find Prince of Persia hiding,” Bar said. Semperis later detected additional command infrastructure behind Cloudflare.